EdgeGate
Industrial Edge Router
THE ROUTER THAT KNOWS WHAT YOUR PLANT IS CARRYING
Most network equipment is designed for offices, then sold to factories afterwards. EdgeGate was designed the other way round — a fanless, DIN-mountable router that replaces the router, firewall, traffic shaper, protocol gateway, remote-access server and compliance logger a site would otherwise need five separate boxes for.
It reads Modbus/TCP, Siemens S7, OPC UA and CoAP natively — polled on a schedule, converted to one common shape, and forwarded on, with no separate protocol gateway and no OPC tunneller licence. Its application catalogue recognises over 40 more industrial and business protocols for traffic prioritisation, from PROFINET and DNP3 to BACnet/IP and MQTT.
Discovery is entirely passive. Sending unexpected traffic to a legacy controller is a documented way to halt a line, so EdgeGate never probes. Every device in its inventory was either volunteered by the device itself or already visible on the wire.
Every firewall rule is default-deny, every change that could cut off its own author applies behind a rollback timer, and every session — remote access, contractor sign-in, configuration change — lands in a hash-chained, append-only record that cannot be quietly edited afterwards.
For estates running more than one site, Sphere Central manages the whole fleet from a single console without owning any configuration of its own. A branch that loses contact with the manager keeps routing, filtering and recording exactly as it was.
Built for the plant floor, not the data centre
One screen, the whole site
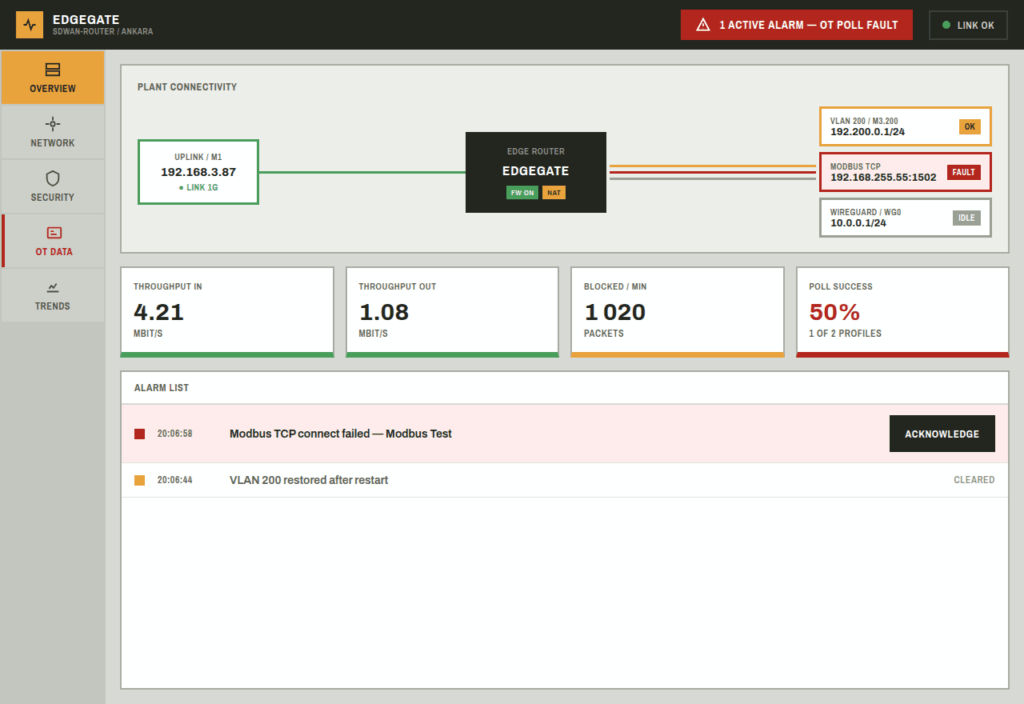
The overview shows the physical uplink, the tagged OT VLAN and any protocol listener — Modbus, OPC UA, tunnels — on one schematic, each with its live status. Throughput, blocked packets and poll success sit alongside a standing alarm list with a target you can hit wearing gloves. Nothing is buried three menus deep.
Default-deny, in plain sight
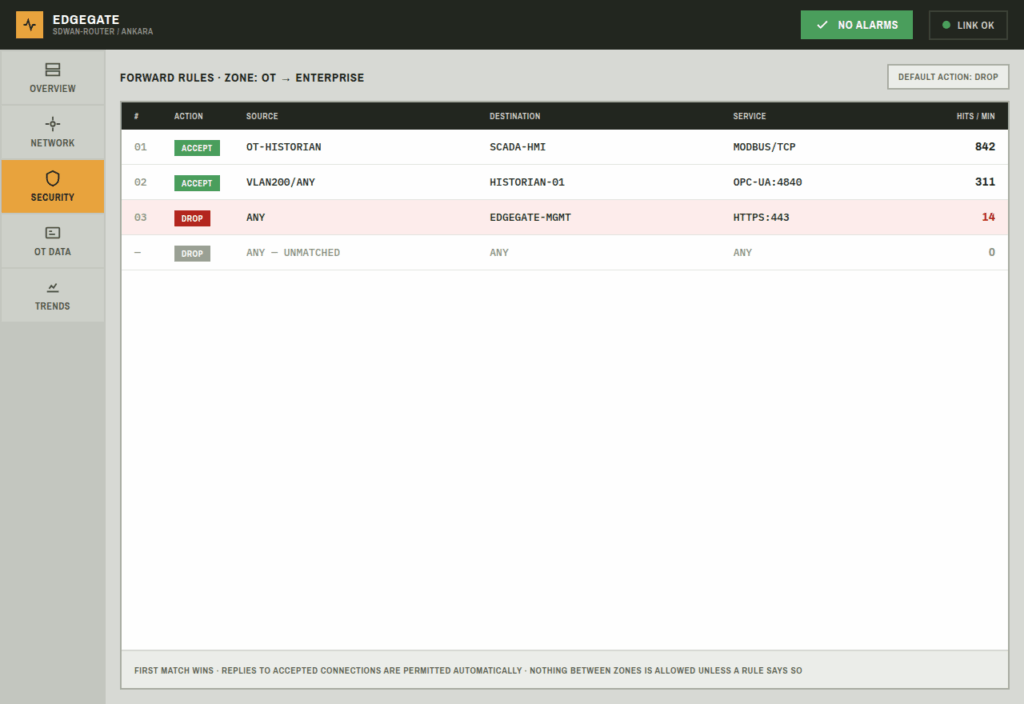
Every forward rule between zones is listed in the order it is actually evaluated — first match wins, and anything unmatched is dropped by default. Live hit counters per rule make it obvious which policies are doing real work and which one just quietly caught something it shouldn’t have. No hidden rule set, no separate manual to cross-reference.